Critical Apache HTTP/2 Flaw CVE-2026-119618: What WordPress Site Owners Should Do
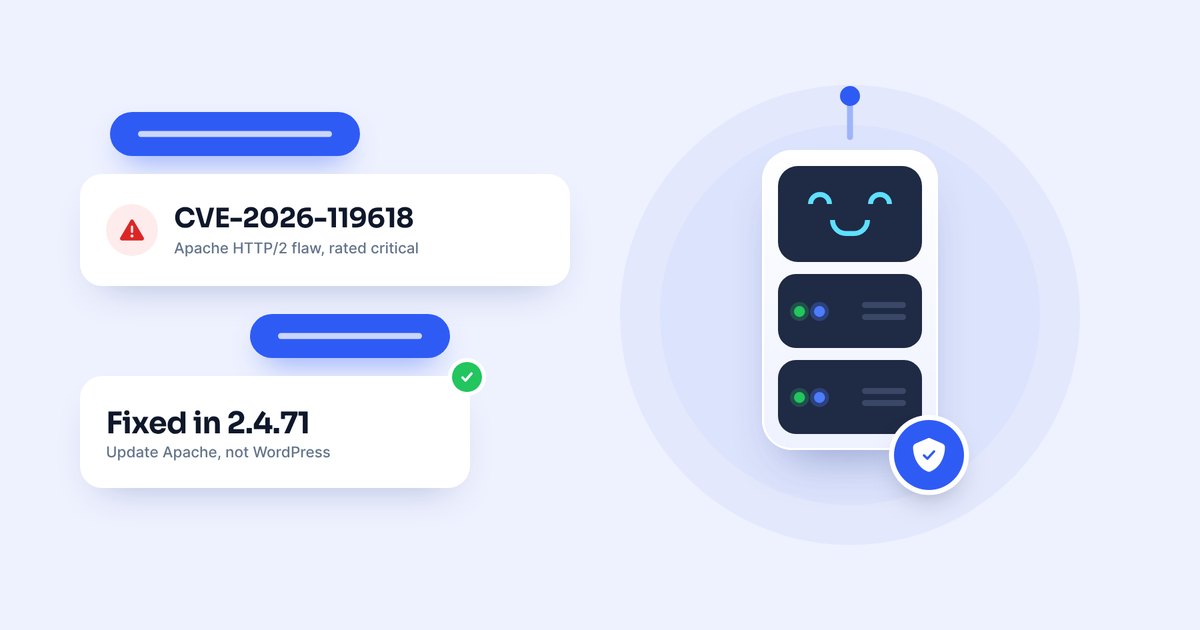
CVE-2026-119618 is a critical flaw in Apache's HTTP/2 module, fixed in Apache 2.4.71. Learn who is affected, why WordPress updates cannot fix it, and how to patch or turn off HTTP/2.